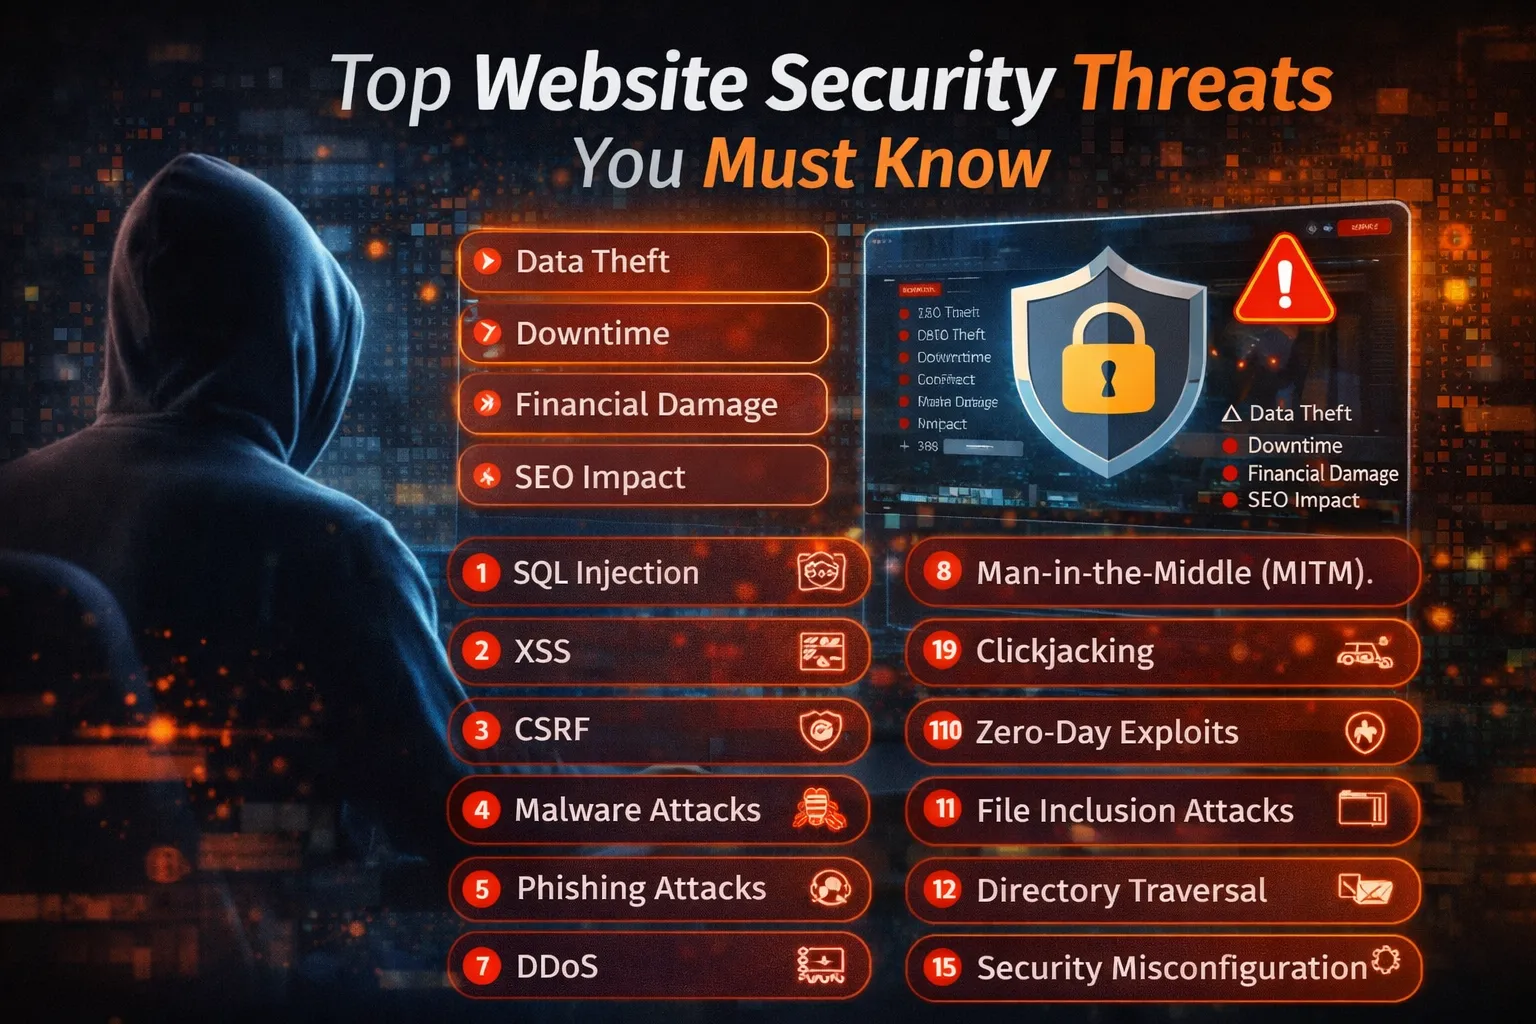
Top Website Security Threats You Must Know
Introduction
In today's connected digital world, websites have become one of the most valuable assets for businesses, organizations, developers, and individuals. From personal blogs and online portfolios to ecommerce platforms and enterprise applications, websites play a critical role in communication, sales, customer interaction, and data management.
However, as the number of websites continues to grow, cyber attacks targeting websites are also increasing rapidly.
Hackers are no longer targeting only large companies. Small websites, personal blogs, startups, and newly launched platforms are also becoming frequent targets because attackers often search for weak security systems, outdated software, and poor configurations.
A single security vulnerability can create serious consequences:
- Loss of customer data
- Website downtime
- Financial losses
- SEO ranking damage
- Reputation problems
- Legal compliance issues
Modern attackers use advanced techniques including automation, artificial intelligence, bot networks, and vulnerability scanners to identify and exploit weaknesses.
In 2026, website security is no longer an optional feature. It is a fundamental requirement for every website owner and developer.
This complete guide explains the most dangerous website security threats, how these attacks work, their impact, and the best methods to protect your website.
Why Website Security Threats Are Increasing in 2026
Cyber threats are becoming more advanced because technology is growing rapidly.
Several factors contribute to the increase in website attacks.
1. Rapid Growth of Online Businesses
Millions of businesses have moved online.
Websites now handle:
- Customer information
- Payment details
- Personal accounts
- Business operations
- Private communications
This makes websites valuable targets for attackers.
A successful attack can provide hackers access to:
- User databases
- Financial information
- Internal systems
2. More Sensitive Data Stored Online
Modern websites store large amounts of information.
Examples:
- Customer names
- Email addresses
- Passwords
- Payment records
- Business documents
- User activity data
Attackers target this information because it can be sold or misused.
3. Weak Security Practices
Many website attacks happen because of basic mistakes.
Common security mistakes:
- Weak passwords
- Outdated plugins
- Poor coding practices
- Missing security updates
- Incorrect server configuration
- No backup strategy
Hackers often do not need advanced techniques when websites have simple weaknesses.
4. Automated Hacking Tools
Modern attackers use automated tools that can scan thousands of websites quickly.
These tools search for:
- Vulnerable plugins
- Weak login systems
- Open ports
- Misconfigured servers
- Outdated software
Even a small website can be discovered automatically.
5. Rise of AI-Based Cyber Attacks
Artificial intelligence has changed cybersecurity.
Attackers now use AI for:
- Creating advanced phishing messages
- Finding vulnerabilities faster
- Automating attacks
- Creating malicious scripts
At the same time, security professionals use AI for:
- Threat detection
- Monitoring
- Automated protection
Cybersecurity has become a continuous battle between attackers and defenders.
How Website Attacks Usually Happen
Understanding attack methods helps developers create stronger protection.
Most website attacks follow similar steps:
Step 1: Discovery
Attackers collect information about a website.
They identify:
- Technologies used
- CMS platforms
- Server details
- Possible weaknesses
Step 2: Exploitation
Attackers attempt to use vulnerabilities.
Examples:
- Injecting malicious code
- Stealing login information
- Uploading harmful files
Step 3: Access
If successful, attackers may gain:
- Database access
- Admin privileges
- Server control
Step 4: Damage
Attackers may:
- Steal information
- Modify website content
- Install malware
- Redirect visitors
- Destroy files
Top Website Security Threats You Must Know in 2026
1. SQL Injection (SQLi)
What Is SQL Injection?
SQL Injection is one of the most common web application attacks.
It occurs when attackers insert malicious SQL commands into website input fields.
Examples of vulnerable areas:
- Login forms
- Search boxes
- Contact forms
- URL parameters
If input is not properly validated, attackers may interact directly with the database.
How SQL Injection Works
A website normally sends user input to a database.
Example:
User enters:
username
password
The application creates a database query.
If the application does not properly protect the input, attackers can manipulate the query.
This may allow them to:
- Read database information
- Modify records
- Delete data
- Bypass authentication
Impact of SQL Injection
SQL Injection can cause:
- Customer data theft
- Password exposure
- Financial damage
- Complete database compromise
For businesses, database leaks can create legal and reputation problems.
How To Prevent SQL Injection
Developers should implement:
Prepared Statements
Use parameterized database queries instead of directly inserting user input.
Example technologies:
- PDO prepared statements
- MySQLi prepared statements
- ORM security features
Input Validation
Always check:
- Data type
- Length
- Format
- Allowed characters
Least Privilege Database Access
Database users should only have required permissions.
2. Cross-Site Scripting (XSS)
What Is XSS?
Cross-Site Scripting occurs when attackers inject malicious JavaScript code into web pages.
The malicious script runs inside another user's browser.
Common XSS Locations
Attackers target:
- Comment sections
- Search results
- User profiles
- Review systems
- Message systems
Types of XSS Attacks
Stored XSS
Malicious code is permanently saved on the server.
Example:
A harmful script stored inside a comment database.
Reflected XSS
The malicious script is sent through a URL or request.
DOM-Based XSS
The vulnerability exists in client-side JavaScript.
Impact of XSS
XSS can allow attackers to:
- Steal cookies
- Hijack sessions
- Redirect users
- Display fake content
- Perform actions as users
XSS Prevention
Use:
Output Escaping
Convert dangerous characters before displaying content.
Content Security Policy (CSP)
CSP controls which scripts browsers can execute.
Input Sanitization
Remove dangerous HTML and scripts.
3. Cross-Site Request Forgery (CSRF)
What Is CSRF?
CSRF tricks authenticated users into performing unwanted actions without knowing.
The attacker abuses the trust between the website and the user's browser.
Example
A user is logged into an online banking website.
The attacker sends a hidden request that transfers money.
Because the browser already has authentication cookies, the website may accept the request.
Impact
CSRF attacks can cause:
- Unauthorized transactions
- Account changes
- Data modification
Prevention
Use:
- CSRF tokens
- Request validation
- SameSite cookies
- User confirmation for sensitive actions
4. Malware Attacks
What Is Website Malware?
Malware is malicious software injected into a website.
Attackers may add harmful code that performs unauthorized activities.
Malware Can Cause
- Data theft
- Spam distribution
- Visitor redirection
- Search engine penalties
- Website blacklisting
Common Malware Sources
- Vulnerable plugins
- Infected themes
- Stolen credentials
- Unsafe file uploads
Prevention
Protect your website using:
- Malware scanners
- Web Application Firewall
- Regular updates
- File monitoring
- Security audits
5. Phishing Attacks
What Is Phishing?
Phishing is one of the most common cybersecurity threats where attackers create fake websites, emails, or messages to trick users into sharing sensitive information.
The attacker creates a website that looks similar to a trusted platform.
Examples:
- Fake login pages
- Fake payment pages
- Fake account verification pages
- Fake password reset pages
The goal is to steal:
- Usernames
- Passwords
- Credit card information
- Personal details
How Phishing Attacks Work
A typical phishing attack follows these steps:
Step 1: Creating a Fake Website
Attackers copy the design of a legitimate website.
They may copy:
- Logo
- Colors
- Login interface
- Branding elements
Step 2: Sending Fake Messages
Users receive messages through:
- Social media
- SMS
- Messaging applications
Example:
"Your account has a security problem. Login immediately."
Step 3: Stealing Information
When users enter their details, attackers capture the information.
Impact of Phishing Attacks
Phishing can result in:
- Identity theft
- Financial fraud
- Account takeover
- Business email compromise
- Customer data exposure
For businesses, phishing attacks can damage customer trust.
How To Prevent Phishing Attacks
Use HTTPS
HTTPS ensures encrypted communication between users and websites.
Enable Multi-Factor Authentication
MFA adds an additional security layer.
Even if passwords are stolen, attackers have difficulty accessing accounts.
Educate Users
Organizations should train employees and customers to identify suspicious messages.
6. Distributed Denial of Service (DDoS) Attacks
What Is a DDoS Attack?
A Distributed Denial of Service attack attempts to make a website unavailable by sending massive amounts of traffic to the server.
Attackers use networks of infected devices called botnets.
How DDoS Attacks Work
Thousands or millions of devices send requests simultaneously.
The server becomes overloaded.
Result:
- Website becomes slow
- Server crashes
- Visitors cannot access the website
Types of DDoS Attacks
Volume-Based Attacks
These attacks consume network bandwidth.
Protocol Attacks
These target server communication protocols.
Application Layer Attacks
These target specific website functions.
Example:
- Search pages
- Login systems
- API endpoints
Impact of DDoS Attacks
Businesses may experience:
- Website downtime
- Lost customers
- Revenue loss
- Reputation damage
For ecommerce websites, even a few minutes of downtime can be expensive.
DDoS Protection Methods
Use CDN Services
A CDN distributes traffic across multiple servers.
Enable Rate Limiting
Limit the number of requests from users or IP addresses.
Use Web Application Firewall (WAF)
A WAF filters malicious traffic before reaching your server.
7. Brute Force Attacks
What Is a Brute Force Attack?
A brute force attack happens when attackers repeatedly try different usernames and passwords until they find the correct combination.
Attackers often use automated tools.
Common Targets
- Admin panels
- WordPress login pages
- User accounts
- Database systems
- FTP accounts
Impact of Brute Force Attacks
Successful attacks can lead to:
- Account takeover
- Data theft
- Website modification
- Malware installation
How To Prevent Brute Force Attacks
Use Strong Passwords
A secure password should include:
- Uppercase letters
- Lowercase letters
- Numbers
- Special characters
Limit Login Attempts
Block users after multiple failed attempts.
Example:
After 5 failed attempts:
- Temporary account lock
- IP blocking
Enable Two-Factor Authentication
2FA significantly reduces unauthorized access.
Change Default Admin URLs
Avoid predictable login locations.
8. Man-in-the-Middle (MITM) Attacks
What Is a MITM Attack?
A Man-in-the-Middle attack occurs when an attacker secretly intercepts communication between two parties.
The attacker positions themselves between:
- User and website
- User and server
Example
A user connects to a fake public Wi-Fi network.
The attacker monitors communication and attempts to steal information.
Information Attackers May Capture
- Login credentials
- Personal information
- Session cookies
- Payment details
How To Prevent MITM Attacks
Use HTTPS Encryption
SSL/TLS protects data transmission.
Avoid Unsafe Networks
Users should avoid entering sensitive information on unknown public Wi-Fi networks.
Use Secure Cookies
Cookies should include:
- Secure flag
- HttpOnly flag
- SameSite protection
9. Clickjacking Attacks
What Is Clickjacking?
Clickjacking tricks users into clicking invisible or hidden elements.
The attacker places a fake interface over a legitimate website.
Example
A user thinks they are clicking:
"Play Video"
but actually clicks:
"Delete Account"
Impact of Clickjacking
Attackers may perform:
- Unauthorized actions
- Account changes
- Permission approvals
Clickjacking Prevention
Use security headers:
X-Frame-Options
Controls whether websites can be displayed inside frames.
Content Security Policy
Frame restrictions can prevent unauthorized embedding.
10. Zero-Day Exploits
What Are Zero-Day Vulnerabilities?
A zero-day vulnerability is a security weakness unknown to developers or vendors.
Because no official fix exists initially, attackers can exploit it before protection is available.
Why Zero-Day Attacks Are Dangerous
They can affect:
- Operating systems
- CMS platforms
- Plugins
- Frameworks
- Server software
Impact
Possible consequences:
- Complete website compromise
- Data theft
- Malware installation
- Unauthorized access
Protection Against Zero-Day Attacks
Although zero-day vulnerabilities cannot always be prevented, risk can be reduced.
Use:
Regular Updates
Install security patches quickly.
Security Monitoring
Monitor:
- Login activity
- File changes
- Server behavior
Web Application Firewall
WAF can block suspicious behavior patterns.
11. File Inclusion Attacks
What Are File Inclusion Attacks?
File inclusion vulnerabilities happen when applications allow users to include unauthorized files.
Attackers exploit poor file handling.
Types of File Inclusion
Local File Inclusion (LFI)
Allows attackers to access files stored on the server.
Possible targets:
- Configuration files
- Password files
- System information
Remote File Inclusion (RFI)
Allows attackers to include files from external servers.
This can lead to:
- Remote code execution
- Malware installation
Prevention
Developers should:
- Validate file paths
- Avoid user-controlled file locations
- Restrict file permissions
- Disable unnecessary features
12. Directory Traversal Attacks
What Is Directory Traversal?
Directory traversal allows attackers to access files outside the intended website directory.
Attackers manipulate file paths to reach restricted areas.
Example
A vulnerable application may allow access to:
- Configuration files
- System files
- Private documents
Impact
Possible results:
- Sensitive data exposure
- Configuration leaks
- Server information disclosure
Prevention
Use:
- Proper file validation
- Access controls
- Safe path handling
- Server security configuration
13. API Attacks
What Are API Security Threats?
Modern websites rely heavily on APIs.
APIs connect:
- Mobile apps
- Websites
- Payment systems
- Third-party services
Poor API security can expose sensitive data.
Common API Attacks
Broken Authentication
Attackers bypass login systems.
Excessive Data Exposure
APIs return unnecessary information.
Rate Limit Abuse
Attackers send excessive requests.
Injection Attacks
Malicious input affects backend systems.
Impact of API Attacks
API vulnerabilities can cause:
- Customer data leaks
- Unauthorized access
- Financial losses
- Service disruption
API Security Best Practices
Use:
Strong Authentication
Examples:
- OAuth
- API keys
- JWT tokens
Rate Limiting
Control request frequency.
Input Validation
Never trust API input.
Monitoring
Track:
- Suspicious requests
- Failed authentication attempts
- Unusual traffic patterns
14. Session Hijacking
What Is Session Hijacking?
Session hijacking occurs when attackers steal a user's active session information.
A session allows users to stay logged in without entering passwords repeatedly.
How Session Hijacking Happens
Attackers may steal sessions through:
- XSS attacks
- Malware
- Unsafe networks
- Stolen cookies
Impact
Attackers may:
- Access user accounts
- Perform actions as the victim
- View private information
Prevention
Use:
Secure Cookies
Cookie settings:
- HttpOnly
- Secure
- SameSite
Session Expiration
Automatically expire inactive sessions.
HTTPS Everywhere
Encrypt all communication.
15. Security Misconfiguration
What Is Security Misconfiguration?
Security misconfiguration happens when systems are incorrectly configured.
This is one of the most common security problems.
Common Examples
- Default passwords
- Exposed database files
- Open server ports
- Debug mode enabled
- Unnecessary services running
Impact
Attackers may gain:
- System information
- Administrative access
- Sensitive files
Prevention
Perform regular security audits.
Best practices:
- Remove unused software
- Disable debug mode
- Change default settings
- Review permissions
- Update configurations
Modern Website Security Challenges in 2026
Website security is becoming more complex because attackers are using advanced technologies.
Major trends include:
AI-Powered Cyber Attacks
Attackers use AI for:
- Automated vulnerability discovery
- Better phishing messages
- Faster attack development
Automated Bot Attacks
Bots continuously scan websites for weaknesses.
Cloud Security Risks
More businesses use cloud infrastructure.
New challenges include:
- Misconfigured cloud storage
- Identity management problems
- API vulnerabilities
Increased API Dependency
Modern applications depend heavily on APIs, making API security more important than ever.
How To Protect Your Website From Cyber Attacks in 2026
Understanding security threats is important, but prevention is the most critical step.
A secure website requires multiple layers of protection.
There is no single security solution that can protect against every attack.
Modern website security follows a defense-in-depth approach, where multiple security layers work together.
1. Always Use HTTPS and SSL Certificate
HTTPS is the foundation of website security.
SSL/TLS encryption protects communication between:
- Website server
- Browser
- Users
Without HTTPS, attackers may intercept sensitive information.
Benefits of HTTPS
HTTPS provides:
✅ Encrypted communication
✅ User trust
✅ Better security
✅ SEO advantages
✅ Protection against data interception
What Information Does HTTPS Protect?
HTTPS protects:
- Login credentials
- Personal information
- Payment details
- Form submissions
- User sessions
2. Keep Website Software Updated
Outdated software is one of the biggest security risks.
Attackers actively search for websites running old versions of:
- WordPress
- Plugins
- Themes
- PHP frameworks
- Server software
Regular Updates Should Include:
CMS Updates
Examples:
- WordPress core
- Joomla
- Drupal
Plugin Updates
Old plugins are common attack targets.
Remove plugins that are:
- Unused
- Unsupported
- Outdated
Server Updates
Keep updated:
- PHP version
- Database software
- Operating system packages
3. Use Strong Authentication
Weak passwords remain one of the easiest ways for attackers to access websites.
Strong Password Rules
A secure password should:
- Be long
- Use unique characters
- Avoid common words
- Not be reused
Example:
Weak:
admin123
Strong:
G7@kP9#vL2!mQ8
4. Enable Multi-Factor Authentication (MFA)
MFA adds another security layer.
Even if a password is stolen, attackers still need another verification method.
Common MFA methods:
- Authentication apps
- Security keys
- SMS verification
MFA Protects Against:
- Brute force attacks
- Password theft
- Unauthorized login attempts
5. Use Web Application Firewall (WAF)
A Web Application Firewall filters malicious traffic before it reaches your website.
WAF Can Block:
- SQL Injection attempts
- XSS attacks
- Malicious bots
- Suspicious requests
- DDoS patterns
Benefits of WAF
- Real-time protection
- Automatic threat detection
- Reduced server load
6. Regular Website Backups
Backups are your safety net.
Even with strong security, problems can happen.
Examples:
- Server failure
- Malware infection
- Accidental deletion
- Failed updates
Backup Strategy
Follow the 3-2-1 backup rule:
3 Copies
Keep three copies of important data.
2 Different Locations
Store backups separately.
1 Offline Copy
Maintain one backup away from the main server.
7. Secure Database Configuration
Databases contain valuable information.
Protect them using:
Limited Database Permissions
Database users should only have necessary permissions.
Change Default Settings
Avoid default:
- Usernames
- Passwords
- Access rules
Encrypt Sensitive Data
Important information should be encrypted.
Examples:
- User information
- Payment details
- Private records
8. Secure File Upload Systems
File uploads are common attack points.
Examples:
- Profile pictures
- Documents
- Images
File Upload Security Practices
Always:
- Validate file extensions
- Check file size
- Rename uploaded files
- Store files safely
- Scan uploads for malware
Avoid allowing dangerous file types:
- .php
- .exe
- .sh
unless absolutely required.
9. Implement Secure Coding Practices
Developers play a major role in website security.
Secure coding prevents vulnerabilities before deployment.
Input Validation
Never trust user input.
Validate:
- Forms
- URLs
- API requests
- File uploads
Output Encoding
Prevent malicious scripts from executing.
Especially important for:
- Comments
- User profiles
- Search results
Secure Database Queries
Use:
- Prepared statements
- Parameterized queries
- ORM security methods
Avoid directly inserting user input into queries.
Error Handling
Do not display sensitive errors publicly.
Avoid showing:
- Database information
- File paths
- Server details
Use custom error pages.
Secure Session Management
Sessions should be protected carefully.
Best practices:
- Use secure cookies
- Set session expiration
- Regenerate session IDs
- Destroy sessions after logout
10. Monitor Website Activity
Security monitoring helps identify attacks early.
Monitor:
- Login attempts
- File changes
- Traffic patterns
- Admin activities
- Server errors
Security Monitoring Can Detect:
- Malware infections
- Suspicious users
- Unauthorized access
- Attack attempts
11. Perform Regular Security Audits
Security should not be checked only after an attack.
Regular audits identify weaknesses before attackers find them.
Security Audit Checklist
Check:
✅ Software versions
✅ User permissions
✅ Database security
✅ SSL configuration
✅ Server settings
✅ Backup system
✅ Login protection
12. Protect APIs
Modern websites depend heavily on APIs.
Secure APIs using:
Authentication
Use:
- OAuth
- JWT
- API keys
Authorization
Users should only access allowed resources.
Rate Limiting
Prevent abuse by limiting requests.
API Monitoring
Track:
- Failed requests
- Suspicious activity
- Unusual traffic
Essential Security Tools for Websites
Website owners and developers can use various security tools.
1. Vulnerability Scanners
These tools identify:
- Security weaknesses
- Outdated software
- Configuration problems
2. Malware Scanners
Detect:
- Malicious files
- Suspicious code
- Website infections
3. Firewall Solutions
Protect websites from:
- Automated attacks
- Bots
- Suspicious traffic
4. Log Monitoring Tools
Analyze:
- Server logs
- Login activity
- Errors
Real-World Impact of Website Security Attacks
A successful cyber attack can create serious damage.
1. Data Loss
Attackers may delete or corrupt important information.
Examples:
- Customer records
- Business files
- Website content
2. Financial Damage
Businesses may lose money because of:
- Website downtime
- Fraud
- Recovery costs
3. SEO Ranking Loss
A hacked website can damage search visibility.
Google may:
- Remove pages from search results
- Display security warnings
- Reduce rankings
4. Customer Trust Problems
Visitors expect secure websites.
Security incidents can damage:
- Brand reputation
- Customer confidence
- Business credibility
Why Developers Must Prioritize Website Security
Developers are the first line of defense.
A secure development approach prevents problems before they happen.
Secure Development Benefits
Security-focused development provides:
- Fewer vulnerabilities
- Better user protection
- Improved reliability
- Easier maintenance
Security Checklist for Developers
Before launching a website:
Authentication
✅ Strong password policies
✅ MFA support
✅ Secure login system
Database
✅ Prepared queries
✅ Limited permissions
✅ Data encryption
Frontend Security
✅ XSS protection
✅ Input validation
✅ CSP headers
Backend Security
✅ Secure APIs
✅ Error handling
✅ Access control
Server Security
✅ Updated software
✅ Firewall enabled
✅ Regular monitoring
SEO Benefits of Website Security
Website security is not only about protection.
It also improves website quality.
Secure Websites Provide:
Better User Experience
Visitors trust websites that are:
- Fast
- Safe
- Reliable
Lower Bounce Rate
Users leave unsafe websites quickly.
Security improves confidence.
Better Search Visibility
Search engines prefer websites that provide safe experiences.
Frequently Asked Questions (FAQ)
What are the biggest website security threats in 2026?
The biggest threats include:
- SQL Injection
- XSS attacks
- Malware
- Phishing
- DDoS attacks
- API vulnerabilities
- Session hijacking
Can small websites be hacked?
Yes.
Small websites are often targeted because they usually have weaker security.
Attackers commonly exploit:
- Outdated plugins
- Weak passwords
- Poor configurations
How can I protect my website from hackers?
Follow security best practices:
- Use HTTPS
- Update software
- Enable MFA
- Use firewall protection
- Backup regularly
- Monitor activity
How often should website security checks be performed?
Security checks should be performed regularly.
Recommended:
- Weekly monitoring
- Monthly audits
- Immediate updates for critical vulnerabilities
Is SSL enough to secure a website?
No.
SSL only protects communication.
Complete security requires:
- Secure coding
- Updates
- Firewalls
- Monitoring
- Backups
Why do hackers attack websites?
Common reasons:
- Stealing data
- Financial gain
- Spreading malware
- SEO manipulation
- Political motives
Are WordPress websites secure?
WordPress itself is secure, but vulnerabilities often come from:
- Outdated plugins
- Weak passwords
- Poor hosting configuration
Proper maintenance makes WordPress much safer.
Final Conclusion
Website security has become one of the most important priorities in 2026.
Cyber attacks are increasing because websites store more data, businesses depend heavily on online platforms, and attackers use advanced automated tools.
From SQL Injection and XSS to malware, DDoS attacks, API vulnerabilities, and zero-day exploits, every website faces potential risks.
However, strong security practices can significantly reduce these threats.
A secure website requires:
✅ HTTPS encryption
✅ Regular updates
✅ Strong authentication
✅ Secure coding practices
✅ Firewall protection
✅ Regular backups
✅ Continuous monitoring
Website security is not a one-time task. It is an ongoing process.
Whether you manage a small blog, an ecommerce store, or an enterprise platform, investing in security protects your users, your reputation, and your digital future.
In 2026 and beyond, website security is not optional — it is a necessity for every successful online presence.
Your email address will not be published. Comments are moderated.
0 Comments on This Post
Leave a Reply
Comments (0)
Spread the Word!
Join Our Developer Community!
Get weekly coding tips, tool updates, and exclusive tutorials straight to your inbox.
Request a Tool
×